

Executive Overview
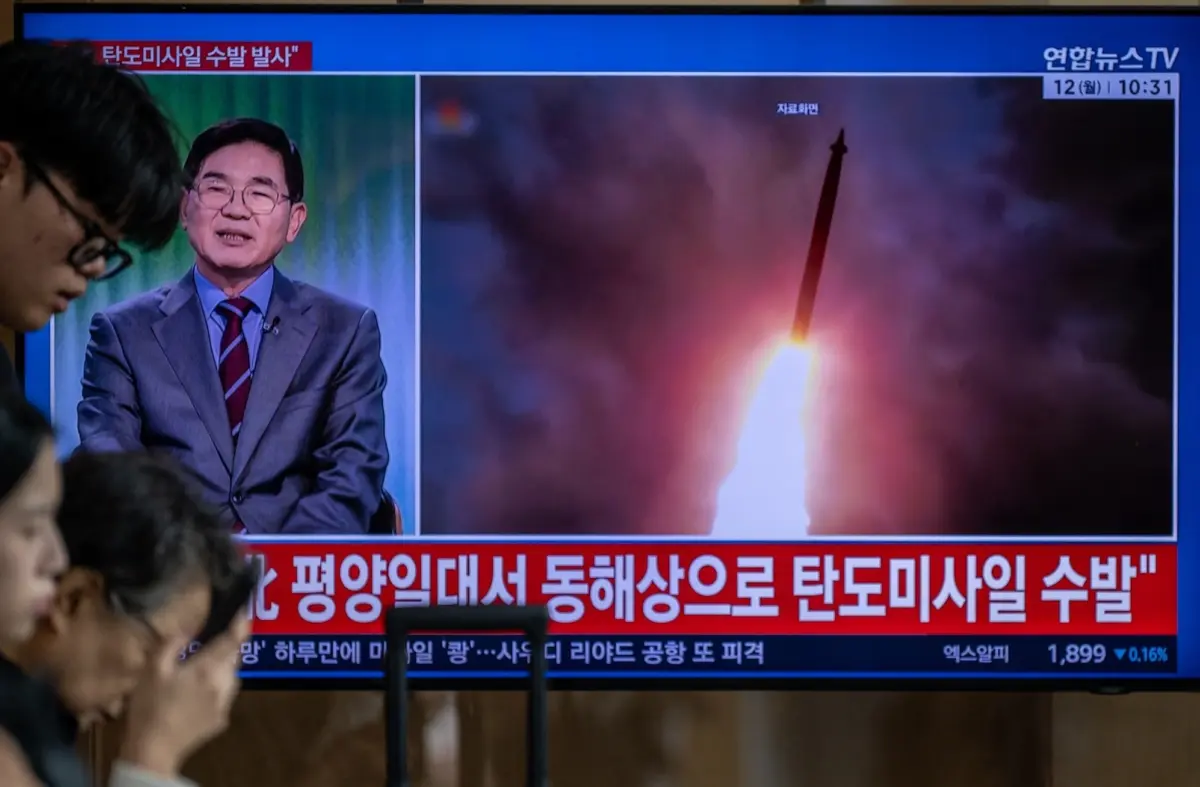
In an escalating cyber espionage campaign that blurs the lines between traditional corporate fraud and state-sponsored warfare, the U.S. Department of Justice (DOJ) has issued an urgent nationwide warning. North Korean state-backed threat actors are increasingly recruiting and exploiting American citizens to facilitate complex, insider-style hacks against United States corporations.
This alarming revelation came to light following a coordinated federal crackdown announced on Tuesday. Federal prosecutors revealed they had indicted and arrested at least two U.S.-based facilitators and executed search warrants across more than 40 residential "laptop farms" spanning the state of Texas. These domestic hubs served as operational relay stations, housing over 180 computers shipped by unsuspecting American companies to remote workers they believed they had legally hired. In reality, these newly onboarded employees were sanctioned North Korean operatives leveraging stolen identities of U.S. citizens to bypass internal corporate defenses.
According to federal law enforcement and cybersecurity partners like CrowdStrike—which assisted the FBI in disrupting the sophisticated operation known as "Famous Chollima"—these laptop farms are vital to Pyongyang. They allow foreign cyber operatives to physically anchor their malicious infrastructure inside the United States, effectively neutralizing the geographical, financial, and legal hurdles of launching cyberattacks from abroad.
To date, investigators estimate that this specific remote IT worker scheme has successfully infiltrated at least 70 U.S.-based companies across Ohio and 16 other states, plus the District of Columbia. Ranging from healthcare and retail to communications, cyber support, and advanced manufacturing, these victim enterprises have collectively suffered millions in direct financial losses, intellectual property theft, and subsequent extortion attempts. However, cybersecurity experts warn that the true scale of the infiltration is likely much broader, pointing to a systemic vulnerability in the modern remote work ecosystem that threatens the foundational integrity of the Western corporate infrastructure.
Detailed Chronology and Enforcement Actions
The dismantling of the Texas laptop farm network represents a critical milestone in a multi-agency federal effort to stem the flow of illicit revenue to the Kim Jong Un regime. For years, federal authorities have monitored the evolution of North Korea’s "remote IT worker" strategy, but Tuesday’s announcements mark one of the most aggressive enforcement actions to date.
The Anatomy of a Texas "Laptop Farm"
The mechanics of the Texas operation expose a sophisticated logistical pipeline built on deception and domestic complicity. According to court documents and DOJ disclosures:
- Identity Theft and Recruitment: North Korean operatives systematically acquire the Personally Identifiable Information (PII) of real U.S. citizens. Utilizing sophisticated spoofed LinkedIn profiles, realistic email addresses, and fabricated video interview setups, they apply for remote technical roles at American companies.
- The American Facilitator: Once hired, the foreign actors require a physical presence inside the United States to receive corporate hardware, handle local banking, and maintain the illusion of a domestic employee. This is where American facilitators enter the equation. At least two primary U.S.-based co-conspirators were identified in Texas, managing over 40 distinct residential locations repurposed as laptop farms.
- The Relay System: When victim companies shipped company-issued laptops and desktop computers to the home addresses of their new "remote employees," the hardware went straight to these laptop farms. The facilitators plugged the computers into local networks and configured them with remote-access software (such as KVM switches and remote desktop protocols).
- The Hands-on-Keyboard Infiltration: Safe behind these domestic IP addresses, the North Korean hackers gained continuous, unhindered "hands-on-keyboard" access to internal corporate networks, exfiltrating sensitive proprietary data, deploying ransomware, and setting up mechanisms for corporate extortion.
Federal authorities seized more than 180 computers during the coordinated Texas raids. Prosecutors emphasized that these actions represent the largest publicly disclosed disruption of residential domestic infrastructure utilized directly by North Korean intelligence and IT syndicates.
Supporting Context & Metrics: A Multi-Billion Dollar Enterprise
The remote IT worker initiative does not operate in a vacuum. It is merely one tentacle of a massive, state-directed cyber-financial machine designed to generate hard currency for North Korea’s internationally sanctioned nuclear weapons and ballistic missile programs.
The Scale of the Infiltration
While the DOJ confirmed that at least 70 companies across 17 states and Washington, D.C., have fallen victim to this specific network—generating roughly $3 million in direct illicit wages and associated theft—independent cybersecurity researchers believe this is merely the tip of the iceberg.
- The FBI Warning: In a concurrent Public Service Announcement (PSA) released via the Internet Crime Complaint Center (IC3), the FBI warned that thousands of North Korean-state-controlled IT workers are currently embedded within Western companies. The bureau categorized these embedded operatives as a "significant national security and intellectual property theft insider threat."
- CrowdStrike Findings: Data compiled by CrowdStrike reveals that North Korean threat actors were responsible for roughly half of all documented "hands-on-keyboard" intrusions over the past year. These are manual, human-driven attacks rather than automated malware scans or AI-driven scripts, reflecting a high degree of operational patience and persistence.
- Broader Financial Crimes: The remote work scheme complements other high-yield cyber operations. Throughout 2025 alone, North Korean state-sponsored hacking groups—such as Lazarus and related state outfits—were implicated in the theft of at least $2 billion in cryptocurrency. Additional major incidents include multi-million dollar crypto exchange heists and sophisticated supply chain attacks targeting the world’s most widely used open-source developer projects.
Sectors Under Siege
The diversity of targeted industries underscores that North Korean hackers are not merely chasing financial ransoms; they are strategically mapping and looting critical sectors of the Western economy. The targeted industries include:
- Healthcare: Exposing sensitive patient data and proprietary medical research.
- Cyber Support & Technology: Positioning rogue actors inside tech firms to weaponize software updates and supply chains.
- Retail & Communications: Compromising consumer databases and critical communications infrastructure.
- Advanced Manufacturing: Stealing industrial designs, trade secrets, and advanced engineering blueprints.
Official Statements and Industry Response
The convergence of private-sector threat intelligence and federal law enforcement has proven vital in exposing how North Korean operatives adapt to corporate security defenses.
In its official announcement, the U.S. Department of Justice highlighted a worrying evolution in North Korean tactics:
"Increasingly, North Korean IT workers are turning to recruiting American facilitators to counter improved private sector detections and law enforcement actions. These workers are hiring facilitators to complete a wider variety of tasks, and in some cases subcontracting entire jobs to third-party foreign nationals."
Cybersecurity firms that aided the investigation emphasized the structural challenges these operations pose. CrowdStrike, in a technical breakdown of the "Famous Chollima" disruption, noted that laptop farms are absolute necessities for the regime:
"Laptop farms are vital to North Korea in helping its hackers overcome physical, financial, and legal challenges of not physically being in the United States." By utilizing domestic intermediaries, these state-backed actors effectively launder their geographic identity, making standard geolocation-based security monitoring nearly obsolete.
Furthermore, the FBI’s IC3 advisory underscored that standard HR vetting procedures—such as remote video interviews and digital reference checks—are no longer sufficient. North Korean actors routinely employ deepfake video technology, altered audio, and paid Western proxies to pass initial screening phases, exploiting the post-pandemic normalization of 100% remote work culture.
Future Outlook: Securing the Remote Workforce
As federal prosecutors move forward with the indictments of the Texas facilitators and forensic experts analyze the contents of the 180 seized computers, the cybersecurity community faces a sobering reality. The weaponization of remote employment models is here to stay, and state-sponsored actors will continue to refine their methods.
Key Takeaways for Corporate Security and Human Resources
- Redefining Background Checks: Companies can no longer rely solely on digital onboarding. Enhanced verification protocols, including mandatory in-person identity validation or cryptographic hardware-key authentication (such as FIDO2/WebAuthn tokens shipped directly to verified physical offices or picked up locally), are becoming essential.
- Monitoring Hardware Logistics: Corporate IT departments must closely monitor the physical destination of company-issued assets. Shipping high-value assets to residential addresses flagged with high turnover, mail-forwarding services, or known multi-tenant virtual offices should trigger immediate internal security audits.
- Behavioral and Network Analytics: Because North Korean IT workers often outsource tasks or exhibit unusual working hours inconsistent with their claimed time zones, behavioral monitoring combined with strict endpoint telemetry can help flag anomalies before sensitive intellectual property is compromised.
The crackdown in Texas sends a clear, unmistakable message to both foreign adversaries and domestic accomplices: the U.S. government views the facilitation of state-sponsored cyber espionage not merely as contract fraud, but as a direct threat to national security. However, until global businesses fundamentally overhaul their remote hiring and endpoint security hygiene, the digital farm gates of America will remain prime targets for Pyongyang’s digital army.
Belum ada komentar. Jadilah yang pertama berkomentar!