For over a decade, migrating credentials from one password manager to another on a mobile device has been a frustratingly friction-heavy chore. Historically, users wishing to switch from Google’s native ecosystem—or any third-party credential manager—to an alternative provider faced a cumbersome gauntlet of exporting sensitive data into unencrypted or poorly protected CSV (Comma-Separated Values) files, saving them to local device storage, navigating file system directories, and manually importing them into a new application.
This archaic process introduced profound security vulnerabilities, including the risk of unencrypted credentials lingering in device download folders, malicious apps scanning storage for credential files, or user error leading to data loss. Furthermore, as the industry marches toward a passwordless future, this legacy migration mechanism broke down entirely when handling modern cryptographic credentials like passkeys, which cannot be easily exported or represented in a simple text-based spreadsheet format.
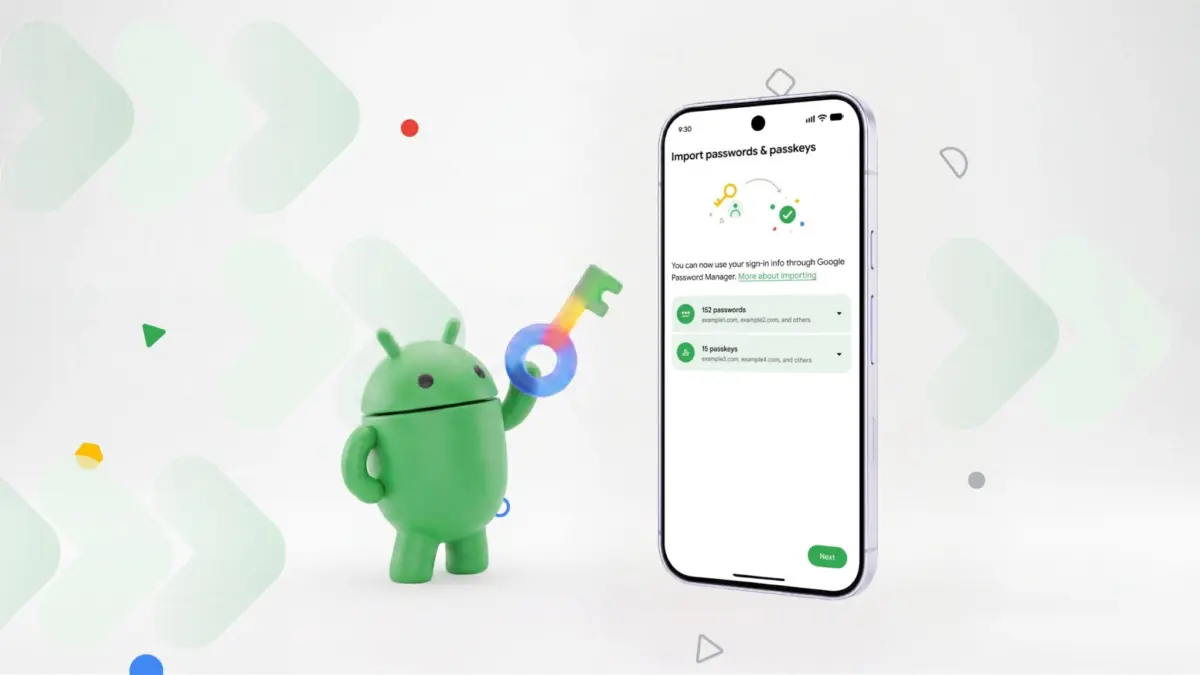
Addressing these critical pain points head-on, Google has officially introduced a revolutionary password manager switching experience for Android. Rolled out in September 2026, this new framework replaces fragile file-based imports with a native, secure, app-to-app communication protocol. Operating seamlessly in the background, the system allows Android users to transfer their entire vault of traditional passwords—and, crucially, their advanced passkeys—between competing applications without ever generating, handling, or exposing a raw data file.
Supported at launch by industry heavyweights such as 1Password, Bitwarden, and Dashlane alongside Google’s own ecosystem, this backward-compatible update spans an impressive range of hardware, working on devices running Android 8 and newer. This comprehensive feature article investigates the mechanics of this rollout, the security implications of moving away from CSVs, the integration of passkey migration, and what this means for the future of mobile credential management.
Detailed Chronology: How the New Migration Protocol Works
The architecture of Google’s new password migration framework is built on Android’s advanced inter-process communication (IPC) capabilities and credential-provider APIs. Rather than forcing applications to serialize user data into portable files, the operating system now acts as a trusted, encrypted intermediary that facilitates a direct, secure handshake between the outgoing and incoming password managers.
Step-by-Step User Journey
Initiation Within the New App: The migration journey begins not inside the settings of the old manager, but directly within the user interface of the newly installed or newly chosen password manager app. The user navigates to the settings menu and selects the option to import or copy credentials from an existing provider.
OS-Level Discovery and Coordination: Upon receiving this command, the new application queries the Android operating system to identify other credential management apps currently installed and active on the device. Android recognizes the request and coordinates a secure data bridge between the two apps using protected system-level channels.
Transparent Review and Approval: Before any data changes hands, a secure system prompt appears on the user’s screen. This interface outlines precisely what data is slated for transfer, offering complete visibility. The user reviews the transfer details and authorizes the operation with a few biometric- or PIN-secured taps.
Direct, Encrypted Transfer: Behind the scenes, the two applications execute a direct, encrypted data payload transfer. The source application packages the credentials securely, and the destination application ingests them directly into its encrypted local database.
Immediate Cleanup and Verification: Once the transfer concludes successfully, the user receives a confirmation notification. Because no intermediate files were ever written to the device’s storage volume, there is nothing left behind to delete, shred, or secure.
This streamlined workflow reduces a multi-step, error-prone manual process—which frequently took non-technical users upwards of fifteen to twenty minutes—into a swift, thirty-second verification loop.
Supporting Context & Metrics: The End of the CSV Era
To understand the magnitude of Google’s engineering update, one must examine the inherent security and usability flaws of the status quo that it replaces.
The Inherent Dangers of CSV Files
For years, the Comma-Separated Values file format served as the universal interoperability standard for password managers. While functional, it was fundamentally unsuited for handling sensitive authentication data:
Plain-Text Exposure: Unless a user explicitly encrypted the CSV file prior to export—a step requiring advanced technical knowledge—all usernames, plain-text passwords, and associated web addresses sat completely exposed in a human-readable format.
Storage Residue: Once generated, CSV files frequently remained dormant in the device’s default Downloads folder indefinitely. This created a persistent honeypot for rogue applications equipped with broad storage access permissions.
Human Error: Users regularly forgot to delete export files after a successful migration, leaving a backdoor to their digital lives sitting in their local file manager.
The Passkey Dilemma
The rise of passkeys—built on WebAuthn and FIDO2 standards—exposed an even greater limitation in file-based migration. Passkeys rely on public-key cryptography stored securely in hardware-backed secure elements or encrypted cloud vaults. A static text file like a CSV cannot capture the cryptographic parameters, private keys, and origin bindings required to make a passkey function.
As a result, early adopters shifting between password managers were forced to abandon their passkeys entirely during migration, manually re-registering each account with every service provider one by one. Google’s new protocol solves this architectural bottleneck by enabling the secure, synchronized transfer of cryptographic key material between certified manager applications, ensuring that users do not lose their strongest authentication credentials when changing software providers.
Market Reach and Compatibility
By anchoring this feature within the Android operating system framework rather than tying it strictly to the latest flagship hardware, Google has maximized its immediate addressable impact. The migration experience is fully supported on all devices running Android 8 (Oreo) and above, bringing advanced credential portability to the vast majority of active Android smartphones and tablets worldwide.
Furthermore, Google collaborated closely with key industry stakeholders from day one. At launch, the system natively supports market-leading third-party password managers, including:
1Password
Bitwarden
Dashlane
Google Password Manager (native implementation)
According to industry analysts, this collaborative approach prevents ecosystem lock-in, aligning with broader regulatory pushes toward data portability and consumer choice in digital software markets.
Official Statements and Industry Reception
The rollout of file-less password migration has drawn widespread praise from cybersecurity experts, privacy advocates, and enterprise software developers alike.
In an official briefing accompanying the release, Google’s Android Security and Privacy engineering teams emphasized that user safety and data minimization were the primary design drivers behind the feature:
"For too long, migrating credentials has felt like a compromise between convenience and security. By establishing a direct, OS-coordinated data bridge between applications, we have eliminated the need for fragile, insecure file exports. Users should be free to choose the password manager that best fits their needs without having to navigate the dangerous waters of unencrypted CSV management. Furthermore, securing passkey migration ensures that users advancing toward modern authentication standards are never penalized for switching apps."
Industry partners integrated into the initial launch echoed these sentiments, highlighting how the frictionless pipeline benefits the broader ecosystem. Representatives from Bitwarden noted that removing migration friction encourages healthy market competition:
"When switching password managers is hard, users stay put out of frustration rather than preference. By streamlining this process securely on Android, Google is empowering users to seek out the best security tools available. We are thrilled to support this standard from day one, offering our users a seamless path to robust, open-source security without compromising on safety."
Cybersecurity analysts have similarly lauded the abandonment of local file storage transfers. In security audits of consumer behavior, poor management of export files consistently ranked among the top vectors for accidental credential leakage during device upgrades or software transitions. By automating and isolating the transfer pipeline inside Android’s secure sandbox, this vector is effectively neutralized.
Future Outlook: The Road Ahead for Credential Mobility
While the launch of native, file-less migration on Android 8+ marks a watershed moment for mobile security, industry watchers are already looking toward the horizon to see how this paradigm will evolve.
Cross-Platform Interoperability and Ecosystem Expansion
One of the most pressing questions facing the developer community is whether this framework can or will be extended across operating system boundaries. While Android devices now possess a streamlined, secure mechanism for app-to-app credential exchange, migrating data between Android and iOS—or between mobile platforms and desktop operating systems like macOS and Windows—still frequently relies on traditional methods or proprietary cloud sync protocols.
Industry consortia and independent security researchers are actively discussing the creation of unified, cross-platform standards for credential and passkey portability. Google’s implementation on Android serves as a powerful proof-of-concept, demonstrating that secure, encrypted, file-less transfers are not only technically feasible but dramatically superior in user experience.
Deeper Integration of Passkey Ecosystems
As passkeys continue to replace traditional passwords across consumer applications, enterprise portals, and financial institutions, the ability to migrate these cryptographic credentials safely will become table stakes for any software claiming to be a complete credential manager. Google’s framework lays the groundwork for standardized passkey export-import protocols that adhere strictly to FIDO Alliance specifications, preventing proprietary lock-in and ensuring that users maintain absolute ownership over their cryptographic identities.
What Consumers and Enterprises Should Do Next
For everyday Android users, taking advantage of this new feature requires simply ensuring that both their current password manager and their newly chosen destination app are updated to their latest respective versions. Users are encouraged to verify that their devices are operating on Android 8 or newer and to explore the import settings within their preferred password management application to experience the new, file-free transition firsthand.
For enterprise IT administrators and security officers, this update signals a positive shift in mobile device management (MDM) and enterprise mobility management (EMM) strategies. Employees transitioning between company-approved security apps can now do so with a drastically reduced surface area for accidental data exposure, streamlining corporate compliance and reinforcing organizational security posture.
As digital threats grow increasingly sophisticated, the elimination of archaic, vulnerable practices like CSV credential exporting represents a vital evolutionary step. By putting user safety, data minimization, and frictionless interoperability at the forefront, Google has redefined the standard for how we manage and move our digital identities.



Belum ada komentar. Jadilah yang pertama berkomentar!