

Executive Overview
In an alarming development for international and domestic travelers alike, Central Japan Railway Company (JR Central) has officially announced a significant data breach affecting its widely utilized Smart EX online ticketing platform. The cyber incident has compromised the personal information of approximately 170,000 registered users, dealing a blow to the perceived security of one of Japan’s most critical transportation ecosystems.
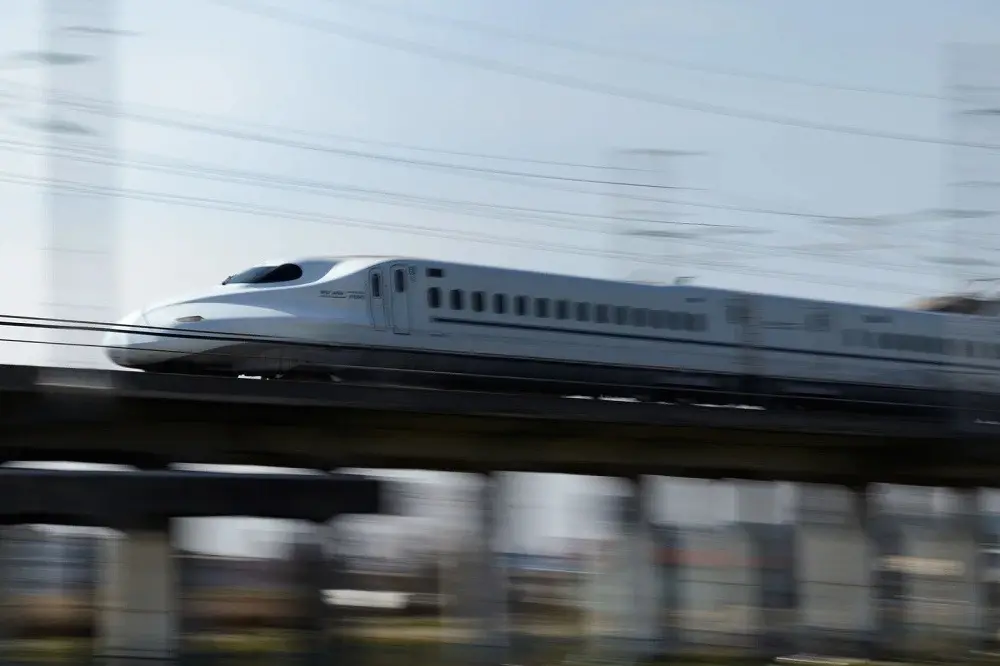
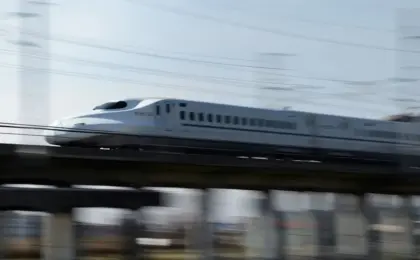
The Smart EX system serves as the digital backbone for Japan’s high-speed rail network, seamlessly managing reservations across the country’s most vital economic and tourism arteries. It bridges operations for JR Central, JR West, and JR Kyushu, encompassing the legendary Tokaido, Sanyo, and Kyushu Shinkansen lines. This sweeping network connects the bustling metropolis of Tokyo through cultural epicenters like Kyoto and Osaka, down through Hiroshima, and all the way to the southwestern terminus of Kagoshima. Because millions of tourists and business commuters rely on Smart EX to book bullet train tickets via credit cards and mobile QR codes, the platform is a prime target for malicious actors seeking high-value consumer data.
According to preliminary investigative findings released by JR Central, the root cause of the breach traced back to a third-party vendor: Yumirulink, a digital marketing and email-forwarding service provider utilized to route specific communications for Smart EX. A security failure within Yumirulink’s infrastructure earlier this month opened the door for unauthorized access, allowing hackers to siphon off restricted user datasets.
While the incident has understandably generated anxiety among frequent travelers, JR Central has emphasized that the scope of the pilfered data is limited. Crucially, highly sensitive financial and personal credentials—such as credit card numbers, billing addresses, phone numbers, and dates of birth—remain secure and uncompromised. Nevertheless, the leak of names, email addresses, and member identifiers still presents significant security risks, including targeted phishing campaigns and credential-stuffing attacks. This report provides an in-depth breakdown of the breach, the timeline of events, the precise nature of the compromised data, official responses, and what affected users must do to safeguard their digital profiles.
Detailed Chronology of the Incident
Understanding how a breach of this magnitude unfolded requires tracing the digital pathways between Japan’s premier railway operator and its ecosystem of third-party digital service providers. The sequence of events highlights the modern corporate vulnerability of depending on outsourced digital marketing infrastructure.
Early October 2026: The Third-Party Vulnerability
The genesis of the breach occurred not within JR Central’s heavily fortified core servers, but rather on the perimeter—specifically at Yumirulink, a specialized digital marketing and email distribution firm. Yumirulink was contracted to handle specific administrative and promotional email dispatches for the Smart EX platform. Sometime earlier in the month, malicious actors identified and exploited a security vulnerability within Yumirulink’s networks.
Mid-October 2026: Detection and Internal Escalation
Upon detecting unauthorized activity and potential data exfiltration within its email-routing pipeline, Yumirulink initiated an internal digital forensics investigation. As the scope of the compromise became clear, the firm alerted its enterprise clients, including JR Central. Railway cybersecurity teams immediately swung into action, isolating affected systems, auditing access logs, and collaborating with external cybersecurity specialists to determine whether direct access to the main Smart EX passenger reservation database had been achieved. Fortunately, investigations confirmed that the breach was contained to the interface managed by the third-party vendor and did not breach the core railway reservation engines.
Public Disclosure and Communication Gaps
JR Central moved to inform the public through formal announcements disseminated via Chukyo TV, Nitele News, and official corporate portals. However, the rollout of the disclosure faced criticism for its fragmented communication strategy. While detailed statements were rapidly published on the Japanese-language iteration of the Smart EX portal, international users navigating the English-language support pages were met with a stark absence of information. This lack of bilingual transparency left thousands of foreign tourists—who heavily rely on Smart EX for navigating the country’s "Golden Route"—unaware that their data might have been compromised.
Supporting Context & Metrics: The Smart EX Ecosystem
To fully comprehend the gravity of this security incident, one must examine the massive scale and operational significance of the Smart EX platform within Japan’s transportation infrastructure.
The Digital Gateway to the Shinkansen
Introduced to streamline ticketing for both domestic commuters and international visitors, Smart EX revolutionized how people board the Shinkansen. Historically, securing a bullet train ticket required physical visits to ticket counters (Midori no Madoguchi) or ticket vending machines. Smart EX replaced this friction-heavy process with an intuitive mobile application and web interface. Users can link their preferred credit cards, select exact car and seat configurations, and generate dynamic QR codes that allow them to breeze through automated ticket gates without ever printing a physical paper ticket.
Geographic Reach and Network Integration
The platform’s reach is formidable, unifying three major operating entities within the Japan Railways Group:
- JR Central (Central Japan Railway Company): Manages the Tokaido Shinkansen, connecting Tokyo, Nagoya, Kyoto, and Osaka. This corridor represents the economic heartbeat of Japan.
- JR West (West Japan Railway Company): Operates the Sanyo Shinkansen, extending the line westward from Osaka through Hiroshima down to Hakata (Fukuoka).
- JR Kyushu (Kyushu Railway Company): Controls the Kyushu Shinkansen, carrying passengers further south from Hakata to Kagoshima-Chuo.
Together, these lines form the spine of Japan’s high-speed passenger transit. Millions of users cycle through the platform annually. Consequently, an exposure affecting 170,000 accounts represents a substantial cross-section of tech-savvy travelers, business executives, and leisure tourists.
Nature of the Dispatched Emails Involved
JR Central was careful to clarify the exact vectors of communication involved in the breach. The company stressed that the incident had no connection to transactional, auto-generated customer service emails—such as automated booking confirmations, seat change alerts, or payment receipts.
Instead, the vulnerability was isolated to communications handled by the third-party email marketer. These included promotional sales campaigns, special announcements, and—notably—system notifications regarding altered timetables and service adjustments following natural disasters, such as the recent Kumamoto earthquake. Because these mass-distribution mailing lists compile user contact details for broad announcements, they served as the repository from which the hackers extracted data.
Analysis of Compromised Data
When news of a data breach breaks, public anxiety instantly gravitates toward financial ruin—fears of drained bank accounts, maxed-out credit cards, and identity theft. In the case of the Smart EX incident, a granular examination of the leaked data reveals a more nuanced, albeit still concerning, picture.
What Was Stolen?
According to official disclosures provided by JR Central, the cybercriminals successfully accessed a tightly scoped package of user information comprising approximately 170,000 individual records. The stolen data fields include:
- User Full Names: Specifically, renderings of users’ names translated into Japanese katakana phonetic characters.
- Email Addresses: The primary point of contact registered to the Smart EX profile, used for receiving notifications and logging into the portal.
- Member IDs / Screen Names: The unique alphanumeric handles chosen by users or generated by the system to identify their accounts.
- Membership Types: Categorizations detailing the specific tier or registration status of the user within the ecosystem (e.g., individual, corporate, or promotional tiers).
What Remained Secure?
In an effort to calm public panic and reassure consumers, JR Central explicitly itemized the categories of sensitive personal data that were not compromised during the intrusion:
- Credit Card Details: Full primary account numbers (PANs), cardholder names, CVV security codes, and card expiration dates were completely shielded from the attackers. Because payment gateways are tokenized and processed through highly isolated, PCI-DSS-compliant financial layers separate from marketing email pipelines, the financial assets of users remain secure.
- Dates of Birth: Personal age and birth data were untouched.
- Home Addresses and Physical Locations: Residential data was not exposed.
- Phone Numbers: Contact telephone numbers linked to accounts were not accessed by the intruders.
The Lingering Ambiguity Over Name Formats
An intriguing wrinkle in the official disclosures involves the specification that only Japanese katakana renderings of names were leaked. JR Central’s initial Japanese-language statements specified that other name formats (such as kanji characters used natively in Japan) were not compromised.
However, digital rights advocates and consumer protection commentators have flagged a troubling ambiguity regarding foreign users. Because the English-language iteration of the Smart EX website failed to publish a corresponding notice at the time of the announcement, it remains unclear whether the "katakana-only" limitation applies to non-Japanese names written in the Latin alphabet (Romanji). If foreign tourist profiles utilized standard English alphabetic characters for their names, it is uncertain whether those records were protected, captured under a different data matrix, or simply omitted from the initial forensic breakdown. This communication gap has drawn criticism from consumer advocates urging greater clarity for international travelers.
Official Responses and Remediation Measures
Corporate accountability and swift incident response are critical metrics by which modern organizations are judged following a cyberattack. JR Central, alongside its vendor partners, has outlined a series of remedial actions designed to mitigate fallout and harden defenses.
Vendor Audits and System Isolation
Immediate containment protocols required Yumirulink to sever infected data-sharing pipelines and shut down the compromised email-routing interfaces. Third-party digital marketing systems have been placed under strict forensic quarantine. JR Central announced that it is conducting comprehensive audits of all external vendors, suppliers, and digital partners who interface with passenger data networks. The objective is to ensure that zero-trust architectures are enforced across the entire supply chain, preventing peripheral marketing tools from maintaining insecure bridges to user databases.
Notifications to Affected Individuals
JR Central has committed to directly notifying all 170,000 affected users via secure channels. Individuals whose email addresses and katakana names were exfiltrated are receiving targeted alerts explaining the nature of the breach and providing customized security guidance.
Recommendations for Smart EX Users
While the absence of leaked financial data is a major relief, cybersecurity experts warn that possessing a user’s name, email address, and member ID is more than enough ammunition for sophisticated social engineering attacks. To protect against secondary exploitation, security analysts recommend the following best practices for anyone who has ever utilized the Smart EX platform:
- Beware of Phishing Campaigns: Armed with your real name and email address, cybercriminals may launch targeted spear-phishing campaigns. They might pose as JR Central or Smart EX, claiming there is an issue with your account, a pending refund, or a required verification step. Never click unsolicited links or input passwords into third-party sites. Always navigate to the official Smart EX portal independently.
- Monitor Secondary Online Accounts: Because many people reuse passwords across multiple platforms, leaked email addresses can be cross-referenced in credential-stuffing attacks. Users should monitor their email, banking, and e-commerce portals for unauthorized login attempts.
- Enable Multi-Factor Authentication (MFA): Where available, users should enforce robust multi-factor authentication across all digital accounts to ensure that stolen credentials alone are insufficient for unauthorized access.
- Keep Financial Statements Under Review: Although JR Central confirmed credit card data was not leaked, practicing vigilant hygiene by reviewing monthly credit card statements for anomalous charges is always a prudent safeguard.
Future Outlook: Cybersecurity Challenges for Japan’s Transit Infrastructure
The Smart EX data breach is far more than an isolated IT hiccup; it serves as a sobering reminder of the complex cybersecurity vulnerabilities facing critical infrastructure operators in an increasingly digitized world.
The Digital Transformation Paradox
Japan has spent the last decade aggressively modernizing its legendary public transportation networks. Initiatives to digitize ticketing, introduce seamless QR code boarding, and integrate multi-modal travel apps have vastly improved convenience for domestic commuters and inbound tourists alike. However, this digital transformation expands the "attack surface" of railway operators. Companies like JR Central—traditionally rooted in civil engineering, mechanical safety, and punctuality—must now evolve into sophisticated cybersecurity organizations capable of defending against state-sponsored hackers, ransomware syndicates, and opportunistic cybercriminals.
Supply Chain Vulnerabilities
As demonstrated by the Yumirulink incident, a corporation’s security posture is only as strong as its weakest vendor. Modern enterprises rely on vast ecosystems of specialized third-party contractors for marketing, customer relationship management (CRM), cloud storage, and email automation. Moving forward, Japanese transportation monoliths will undoubtedly face mounting pressure from regulators—such as the Personal Information Protection Commission (PPC)—to enforce rigorous, continuous compliance audits on every external partner granted even peripheral access to passenger data.
Rebuilding Consumer Trust
For international travelers preparing to visit Japan and experience the world-famous "Golden Route," platform confidence is paramount. The initial stumble in bilingual communication regarding the Smart EX breach highlights an urgent need for Japanese corporations to adopt globally inclusive, instantaneous crisis communication frameworks. Ensuring that foreign visitors receive transparent, timely alerts in English and other major languages is essential for preserving trust in Japan’s tourism infrastructure.
Ultimately, while the Smart EX breach could have been catastrophic—had core financial vaults and credit repositories been breached—the exposure of 170,000 personal profiles is a wake-up call. It underscores the reality that in the 21st century, securing the rails requires just as much vigilance in cyberspace as it does on the physical tracks.
Belum ada komentar. Jadilah yang pertama berkomentar!